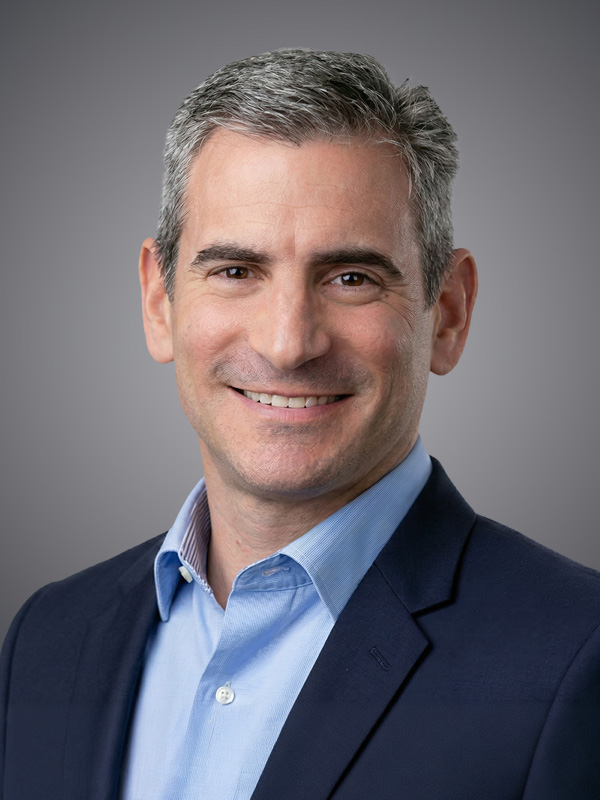
Michael Savitz is a Director at Aletheian Labs with over 18 years of experience working on digital forensics and incident response investigations within both the public and private sectors.
Much of Michael’s work involves stepping into situations where the facts are still developing. He analyzes systems, logs, and network activity to determine how access was established, what happened inside the environment, and how events played out over time.
Michael has led complex investigations involving theft of trade secrets, ransomware, business email compromise, and unauthorized access across a broad client base, including government agencies, mid-market companies, and Fortune 50 enterprises.
Before joining Aletheian Labs, Michael held senior roles at Palo Alto Networks’ Unit 42. Earlier in his career, he spent a decade as a digital forensic examiner at Booz Allen Hamilton, conducting hundreds of examinations for counterintelligence and counterterrorism.
- Incident-driven investigations and event reconstruction
- Ransomware and intrusion analysis
- Business email compromise matters
- Analysis of endpoint, network, and cloud activity
- Reconstruction of timelines from incomplete data
Led investigations involving ransomware and advanced intrusions, analyzing endpoint, network, and cloud data to determine how access was established and how activity progressed through the environment
Conducted forensic analysis in matters involving business email compromise and insider threat, reconstructing user activity to understand what actions were taken and when
Managed large-scale investigations for enterprise organizations, overseeing forensic analysis and coordinating with legal and executive stakeholders to keep findings aligned
Performed forensic examination across endpoints, mobile devices, and cloud environments to identify and recover relevant evidence across multiple data sources
Supported counterintelligence and counterterrorism investigations through direct analysis of digital evidence and investigative reporting
Testified as a digital forensics expert regarding email artifacts and system access in a high-stakes M&A dispute