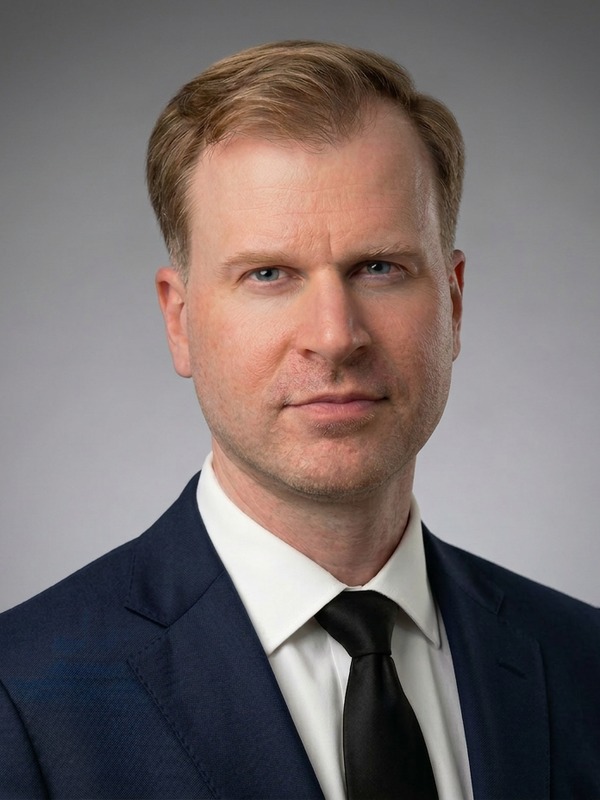
Jonathon Tomczak is a Director at Aletheian Labs with more than 20 years of experience in digital forensics, incident response, and systems development. His background combines forensic investigation with software development, giving him a practical understanding of both the evidence investigators rely on, and the systems used to find and analyze it.
Throughout his career, Jonathan has developed forensic and data analytics tools used by cybersecurity firms and organizations around the world. He has also led investigations involving intrusions, insider threats, and fraud, and has conducted compromise assessments for large organizations during mergers and acquisitions. His experience extends to enterprise IT infrastructure and SCADA environments.
Before joining Aletheian Labs, Jonathan held senior roles at CrowdStrike, Crypsis, and Mandiant. Earlier in his career, he cofounded TZWorks, where he led the development of forensic tools for law enforcement and enterprise users. He also taught incident response and digital forensics to government and private-sector teams and presented at international conferences, including SANS DFIR Prague, BruCON, and SANS Summits.
- Digital forensics and incident response
- Forensic tool and systems development
- Cybersecurity investigations and compromise assessments
- Insider threat and fraud investigations
- Enterprise IT and SCADA environments
- Data collection and forensic analytics
- AI-assisted cybersecurity and forensic workflow
Served as a third-party cybersecurity subject matter expert supporting PricewaterhouseCoopers on complex digital forensics, incident response, compromise assessment, and security architecture matters
Led compromise assessments associated with Fortune 500 mergers and acquisitions, evaluating enterprise environments and identifying security risks affecting post-transaction integration
Designed and deployed cloud-based forensic pipelines supporting Windows, Linux, and macOS environments, significantly improving the speed of evidence collection, processing, and investigative triage
Architected a high-performance data aggregation platform capable of sub-second queries across billions of security events in support of digital forensics, incident response, threat hunting, and anomaly detection
Developed forensic collection, metadata analysis, timeline reconstruction, and high-volume data-processing tools used by investigators and incident responders in enterprise environments
Led and conducted incident response and forensic investigations involving sophisticated intrusions, insider threats, and compromised enterprise systems across multiple industries