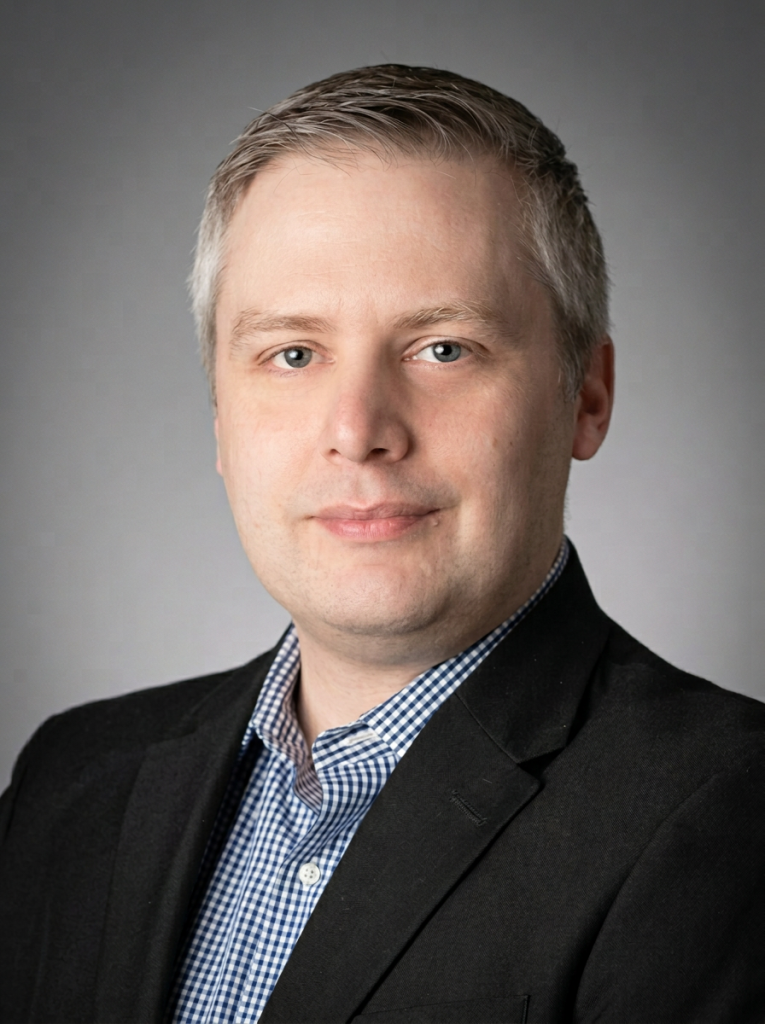
Kevin Faulkner is a cofounder of Aletheian Labs and a seasoned digital forensics expert with more than 25 years of experience working with complex systems and digital evidence.
Kevin’s work is centered on understanding how data moves through systems and what that activity reveals. He examines user behavior, system interactions, and underlying data to piece together what happened, how information was accessed or transferred, and whether those actions align with what has been represented.
Kevin has worked on matters involving trade secret misappropriation, data loss under legal hold, document authenticity, and the behavior of systems across both networked and hardware environments. He regularly serves as a testifying expert and has provided affidavits, expert reports, and testimony in depositions, hearings, and trial.
Before cofounding Aletheian Labs, Kevin was Vice President at Palo Alto Networks’ Unit 42, where he led and testified in complex forensic matters and provided expert testimony. He previously served as a managing director at Stroz Friedberg, where he led the national digital forensics and incident response practice and oversaw technical operations across a wide range of investigations.
- Digital forensics and system analysis
- Trade secret and data misappropriation matters
- Analysis of data movement across systems and devices
- Document authenticity and electronic evidence
- Expert witness testimony
Led forensic analysis of payment terminal hardware and network traffic to determine what was transmitted, where it was sent, and how the systems were functioning in response to a government inquiry
Testified in a federal jury trial regarding the analysis of trade secret data, including how sensitive information was copied, transferred, and used
Conducted forensic analysis of embedded credit card skimming devices, including hardware examination and recovery of stored card data through chip-level extraction techniques
Led investigation of network intrusions and malware activity, analyzing system artifacts and network traffic to determine attacker behavior, system access, and potential data exfiltration
Performed independent forensic analysis of previously examined systems, identifying additional devices and evidence relevant to ongoing investigations
Conducted analysis of large-scale data environments, including databases and legacy systems, to locate and interpret information that was not readily visible through standard review methods